"Plan for Your Key Providers to Fail": A Cybersecurity Expert on This Week's Outages and the ARTEX Warning
By Devakumar A/L Robert William, Senior Executive, BAC College and Nevash Nithi, Content Writer, BAC College

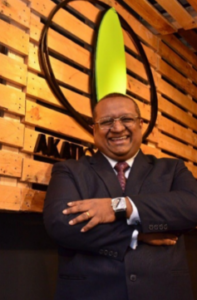
Krishna Rajagopal, CEO of AKATI Sekurity and Adjunct Professor of Practice at UNIMY, answers five questions for our students, parents and partners.
It has been a worrying week for technology. Last Friday, flights across the US were grounded for hours, which the US aviation authority traced to a single router in Arkansas. On 12th and 13th November 2026, a global Microsoft 365 outage left people unable to use Outlook and Teams for nearly 24 hours. This week, the US National Security Agency’s internal classified network was disrupted, which the agency described as temporary degradation during scheduled maintenance.
At the same time, the FBI has warned in a FLASH advisory that criminals and state-aligned hackers are using ARTEX, an AI-powered penetration testing framework, to automate attacks. The FBI says some intrusions went from first targeting to privileged access in under three hours.
Are these events connected? What should we do? We asked Adjunct Professor Krishna Rajagopal, our Adjunct Professor of Practice.
About Adjunct Professor Krishna Rajagopal
With over two decades of experience, Adjunct Professor Krishna Rajagopal is a globally recognized expert in cybersecurity, digital forensics, and information security standards. He is a member of the ISO IEC JTC1/SC27/WG4 committee and has played a pivotal role in shaping international cybersecurity benchmarks.
Krishna has trained military officers under the US Military Pacific Command (USPACOM MCIP) and consulted police forces worldwide on cybercrime investigations. He is the author of “The Cybersecurity Powerplay – A Boardroom Guide to Digital Defense” and has served as an expert witness in high-profile cases, including in the UAE.
He holds over 50 professional certifications, including CISM, CEH, and SWIFT CSP Independent Assessor, and was the youngest MCSE in his country. His operational expertise includes leading over 500 successful Penetration Tests and Red Team exercises across critical sectors.
Krishna is the Founder and CEO of AKATI Sekurity, under whose leadership the company has earned numerous accolades, such as:
· Cybersecurity Excellence Awards
· MSSP Alert Top 250 MSSP – Ranked Top 12 Globally
· Channel Futures MSP 501 – Top 10 Rankings
· Frost & Sullivan Asia-Pacific Strategy Leadership Award
He was honored with the “Distinguished Engineer” title by Rocheston, New York, and received the TIMES Group Power Icon 2024 Award as Digital Forensic Investigator of the Year.
A sought-after speaker, Krishna has delivered impactful presentations globally, including in South America, where his sessions attracted over 1,000 attendees nightly. His ability to simplify complex cybersecurity topics has made him a respected voice in the industry.
Connect with Adjunct Professor Krishna Rajagopal: Follow him on LinkedIn for more cybersecurity insights: https://www.linkedin.com/in/mykrishnarajagopal/
Follow AKATI Sekurity on LinkedIn for the latest from his team: https://www.linkedin.com/company/1518348/
1. Are these incidents connected, or is it mostly coincidence and complex systems failing?
I think it is mostly coincidence and complex systems failing. Microsoft says three factors combined: a software defect in its gateway servers, extra traffic from a routine Teams failover, and about 14 per cent of capacity already down for an unrelated reason. The FAA disruption was linked to faulty networking equipment, and the NSA cited scheduled maintenance. CNN’s sources said there was no evidence of a cyberattack on NSANet.
I would not close the door yet. The NSA cause is still unexplained. But nothing public links these outages to ARTEX. ARTEX leaves a different footprint. It goes after exposed apps, weak credentials, and cloud app permissions. The Optimizely code injection was a real attack, but it is a separate event. Either way, the lesson holds. Plan for your key providers to fail.
2. What does AI-powered attack tooling like ARTEX change for defenders?
It changes speed and scale. It does not change the techniques. The FBI lists flaws we have known for years: unsigned SAML assertions, SQL injection, missing API authentication, and admin passwords hardcoded in JavaScript. ARTEX finds them faster and works on many targets at once. Some intrusions reached privileged access in under three hours. It also lowers the skill needed to attack.
The tool connects to outside AI models, including Claude, GPT, and DeepSeek. The FBI says attackers favour Chinese models, led by DeepSeek Flash, because they showed no observable guardrails when the task was framed as penetration testing.
For defenders, this means three things. Close basic flaws in days, not months. Cover every machine with endpoint protection. The attackers checked which Windows machines lacked CrowdStrike Falcon, and endpoint protection blocked their lateral movement. Finally, give every alert an owner who can act within minutes.
3. What should Malaysian businesses and institutions do now?
Start from the fact that NACSA raised the national threat level from low to moderate on 4th November. Asian financial institutions are already targets, as the South Korean bank campaign shows.
First, know what you expose. List every internet-facing system, including supplier portals, sales-support tools, and apps that business units built on their own. Second, lock down the management layer. Cloud admin, backup platforms, and hypervisors belong on trusted networks only. Third, scan your code and pipelines for embedded passwords and rotate what you find. Review your Entra logs for new app credentials, consent grants, and role changes. Keep those logs, along with your SIEM data.
Watch for unexpected outbound calls to AI services from systems that have no reason to make them. If you use ConnectWise Cloud Backup, review every Microsoft 365 tenant where its apps are or were installed, from 1st October onward. Keep those connections disabled until ConnectWise gives restoration steps. Report anomalies to NACSA’s NC4.
4. What simple steps should students and parents take to protect themselves?
Assume some of your personal data is already out there. The South Korean campaign took data on about 67,000 people. Criminals use names, phone numbers, and financial details to make scams sound real. NACSA expects more AI-driven scams, phishing, and credential theft.
So the habits matter more than the tools. Turn on multi-factor authentication with an authenticator app. Use a password manager and a different password for every account. Turn on automatic updates. Never share a one-time code with anyone. If a message creates urgency, stop and call the person on a number you already have. Check bank accounts and phone numbers on PDRM’s Semak Mule before you pay. Agree on a family code word. Parents, tell your children to report a problem fast, with no blame.
5. What does this mean for students thinking about a cybersecurity career?
It means the entry point is changing. ARTEX automates reconnaissance and the exploitation of basic flaws. That is junior testing work, so expect fewer roles built only on it. Demand grows for people who can read cloud and identity logs, scope an incident, preserve evidence, and decide how to contain it. The FBI is asking defenders for exactly those skills.
World Bank data cited by The Star shows Malaysia has about 3,000 AI professionals against projected demand of roughly 30,000 by 2030. Security demand follows AI adoption.
My advice is simple. Learn networking, identity systems such as Active Directory and Entra, cloud basics, and one scripting language. Build a home lab. Use AI tools every day and learn where they fail. Practise explaining a finding to a board. That skill will set you apart.
Closing
Prof Krishna’s message is clear: the techniques are old, but the speed is new, so the basics matter more than ever. If this made you curious about how to defend systems like these, our Cybersecurity programme is a good place to start. https://www.unimy.edu.my/cybersecurity-digital-defence/