From Systems Engineering to Cybersecurity Leadership: Prof. Abbas Kudrati on Careers, AI and the Future of Security
By Devakumar A/L Robert William, Senior Executive, BAC College and Nevash Nithi, Content Writer, BAC College
Technology is changing rapidly, and building a career in the industry can sometimes feel overwhelming. There are new tools to learn, new skills to develop and growing questions about how artificial intelligence will change the jobs available.
For students considering a career in technology, and working adults thinking about making a career change, knowing where to begin can be just as challenging as keeping up with the industry.
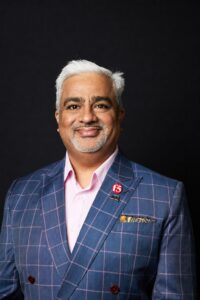
As part of the UNIMY Expert Interview Series, we speak with Prof. Abbas Kudrati, Field Chief Information Security Officer (CISO) for Asia Pacific, China and Japan at F5, Professor of Practice at La Trobe University, author of six books and technical editor of several more and Microsoft Most Valuable Professional (MVP).
With nearly three decades of experience spanning systems engineering, consulting, technology and cybersecurity leadership, Prof. Kudrati shares practical advice on entering the industry, developing valuable skills, gaining hands-on experience and understanding the opportunities emerging from AI.
1. You began your career in systems and network engineering. What led you towards cybersecurity, and how did your career develop into leadership roles?
The technology industry has evolved considerably over the course of my career. What was once commonly referred to as IT security developed into information security and, eventually, the broader field of cybersecurity as organisations became increasingly dependent on digital systems.
My own path into security was gradual. I started in 1997 as a systems administrator, then moved into network engineering and IT audit. Audit changed the question I asked. Instead of asking whether a system worked, I began asking what would happen if someone misused it. By around 2004, I had moved fully into security, and that question has shaped every role since, from consulting in the Middle East to serving as a government CISO in Bahrain to advising executives across Asia Pacific today.
My career took me through different areas of technology, including systems engineering, consulting and technology leadership. Working with organisations such as KPMG, Ernst & Young and Microsoft, and later with F5, gave me exposure to different perspectives on technology, business operations and risk.
These experiences helped me understand that cybersecurity is not simply about implementing technical controls. It also involves understanding how an organisation operates, what it needs to protect and how security decisions affect its ability to achieve its goals.
One important lesson is that security should enable a business to move forward confidently. I often compare it to the brakes in a car. Good brakes allow a driver to travel faster with greater confidence because the driver knows the vehicle can slow down safely when necessary.
In the same way, effective security gives organisations greater confidence to adopt new technologies, develop services and innovate while managing risk. The best security teams are not known for saying no. They are known for making yes possible.
2. For school leavers and university students, what should they learn first if they want to pursue a career in cybersecurity?
My advice is to build your knowledge in stages rather than trying to learn everything at once.
Start with the fundamentals of IT. This includes understanding operating systems, networking concepts such as TCP/IP, DNS and HTTP, and how Linux works. Learning some scripting is also valuable because it helps you understand how tasks can be automated.
Once you have a foundation, begin exploring core cybersecurity principles. These include identity and access management, encryption, vulnerability management and secure system configurations.
The next step is to practise. Set up a home lab, experiment with virtual machines and use guided learning platforms such as TryHackMe to develop your skills in a controlled environment.
You can then explore programming and automation using tools and technologies such as Python, the query languages used by security tools, such as KQL or SPL, and APIs. These skills can help security professionals investigate information, work with data and automate repetitive tasks.
After developing these foundations, consider specialising in an area that interests you, such as cloud security or identity security.
The important thing is to follow a learning path. Build your fundamentals first, practise what you learn and specialise when you have a better understanding of the field. I think of it as five stages: foundations, principles, practice, automation and specialisation.
3. Is it too late for working adults or people without an IT background to move into cybersecurity?
People from non-IT backgrounds can bring valuable skills to cybersecurity. A person’s previous education and work experience do not necessarily have to become irrelevant when they enter the technology industry.
For example, during my time at Microsoft, I observed how military veterans were hired to work in Security Operations Centre (SOC) teams. Their military backgrounds brought valuable qualities to the role, including the ability to remain calm under pressure and respond to challenging situations. This illustrates how skills developed outside traditional IT careers can also be valuable in cybersecurity.
Someone with an accounting or finance background may already understand budgets, financial controls and the importance of managing resources. These skills can be useful when making security investment decisions, evaluating vendors or managing cybersecurity budgets.
People from other fields can also contribute different perspectives. Experience in areas such as law or psychology can help professionals understand legal requirements, human behaviour and the ways people interact with technology.
The key is to build on those existing strengths while developing the technical knowledge needed for the role.
A career change still requires effort and preparation. Someone without an IT background may need to start with basic computing, networking and security concepts before moving into more specialised work.
My advice is to identify the skills you already have, understand what the industry requires and develop a practical plan to bridge the gaps.
You do not necessarily need to discard your previous experience to enter cybersecurity. In many cases, the combination of technical knowledge and experience from another field can become an advantage.
4. AI is changing both cyberattacks and cyber defence. What skills will matter most, and how can students prepare for AI security?
AI is a technology that can be used by both attackers and defenders. It can help security teams analyse information and automate certain tasks, while also giving attackers new ways to scale activities such as social engineering.
Students often ask me whether AI will replace entry-level security jobs. My answer is that it will replace many entry-level tasks. Triaging large volumes of alerts, writing basic queries and summarising logs are already being automated. What AI cannot do is judge what truly matters, explain risk to a business leader or take accountability for a decision. So build that judgement early. Learn to ask why an alert matters, not only how to close it.
For students interested in AI security, I would still begin with strong cybersecurity fundamentals. AI systems operate on existing technology infrastructure, so understanding networks, systems, access controls and data security remains important.
The next step is to develop a basic understanding of how machine learning and large language models work. You do not necessarily need to become an AI researcher, but you should understand what these systems do, how they can fail and where their limitations lie.
It is also important to understand risks specific to AI applications. These include prompt injection, where malicious instructions attempt to manipulate an AI system, and data leakage, where information is exposed inappropriately.
As AI systems become more capable of taking actions through connected tools and services, securing AI agents and controlling the access they receive will also become important. Every AI agent that acts on our behalf needs an identity, permissions and oversight, just like an employee. Securing these non-human identities will be one of the fastest-growing specialisations of the next decade, and students who understand both identity and AI will be rare and valuable.
Finally, learn to use AI responsibly. AI-generated answers and code should not be accepted blindly. You need to evaluate the output, verify important information and understand the consequences of putting it into practice.
AI will continue to change the cybersecurity landscape, but a sound understanding of security principles will help professionals adapt as new technologies emerge.
5. What is a common misconception about cybersecurity careers, and what does the work actually involve?
One common misconception is that cybersecurity is all about hacking.
Although ethical hacking and penetration testing are important parts of the field, cybersecurity offers many other career paths. These include security operations, security engineering, governance, risk and compliance, and security leadership.
This is especially relevant in Malaysia. The Cyber Security Act 2024 requires organisations that operate national critical information infrastructure, in sectors such as banking, healthcare, energy and transport, to conduct regular risk assessments and audits and to report cyber incidents. That creates demand not only for technical specialists but also for people who understand governance, risk and compliance.
Different roles involve different responsibilities. Some professionals investigate suspicious activity and respond to incidents. Others design secure systems, assess vulnerabilities, establish policies or help organisations understand and manage risk.
Cybersecurity also requires collaboration. Security professionals need to communicate with technical teams, business leaders and other stakeholders to make sure security measures are practical and appropriate.
Another misconception is that it is possible to achieve 100 per cent security. No organisation can eliminate every risk.
The more realistic objective is resilience: being able to identify threats, detect problems, respond effectively and recover when an incident occurs.
Security professionals must therefore think beyond preventing attacks. They also need to help organisations prepare for the possibility that something may go wrong.
6. How can beginners gain hands-on experience, and are certifications enough to secure their first job?
Certifications can help demonstrate that you have studied a subject and developed knowledge in a particular area. However, certifications alone do not necessarily show an employer how well you can apply that knowledge.
Practical experience is especially important for someone seeking their first job in technology.
You can begin by building a home lab, working with virtual machines and completing guided exercises. These activities allow you to experiment with technology, make mistakes and understand how systems behave. Capture the Flag (CTF) competitions, local security community meetups and internships are also excellent ways to sharpen your skills and meet the people who hire.
You can also document your work through a GitHub repository, a technical blog or a portfolio of projects. This gives employers something concrete to examine when assessing your abilities.
For example, rather than simply stating that you have studied identity security, you could document a lab that explores how user accounts, permissions and access controls work. Explain what you built, what you learned and what you would improve.
The value lies not only in completing the project but also in being able to explain your decisions and demonstrate your understanding. Being able to explain what you did in plain language is a skill that sets candidates apart.
You should also look at real job descriptions. Identify the technologies, skills and experience employers are asking for, then use those requirements to guide your learning.
Certifications can form part of that journey, but they should complement practical work rather than replace it.
7. After decades in the technology industry, what advice would you give someone starting their career today?
Never stop learning.
Technology changes continuously, so professionals need to remain curious and willing to develop new skills throughout their careers. You cannot expect what you learned at the beginning of your career to be sufficient for the rest of your working life.
At the same time, you do not need to learn everything. Build a strong foundation, understand your interests and keep developing the skills that are relevant to your chosen direction.
Be flexible when opportunities arise. Sometimes progressing in your career means exploring a new area, taking on a different responsibility or moving beyond what is familiar.
My own career is an example. I did not start in security. Each move I made, from systems administration to networking, audit, security and executive advisory work, felt like starting over. It never was. Every layer built on the one before it.
I also believe experienced professionals should contribute to the wider community. As you develop your knowledge, consider mentoring others, teaching, writing or sharing what you have learned. Helping others grow can be a meaningful part of a long career.
Ultimately, a successful technology career requires more than keeping up with tools. It requires curiosity, adaptability, practical experience and a willingness to keep learning.
Key Takeaways
Prof. Abbas Kudrati’s career journey highlights several lessons for anyone considering a future in technology or cybersecurity.
Build your foundations before specialising. Learn how operating systems, networks and other core technologies work before moving into advanced security topics.
Make practical experience a priority. Home labs, guided exercises and documented projects help turn theoretical knowledge into skills you can demonstrate to employers.
Recognise the value of your existing experience. People moving from non-IT backgrounds can bring useful knowledge and perspectives into cybersecurity, provided they also develop the necessary technical skills.
Learn about AI without neglecting cybersecurity fundamentals. Understanding AI-related risks is increasingly important, but strong knowledge of systems, networks, access controls and data security remains essential.
Build judgement, not just skills. AI will automate many entry-level tasks. The ability to decide what matters, explain risk and take ownership will become more valuable, not less.
Think beyond hacking. Cybersecurity includes technical, operational, governance and leadership roles, offering different paths for people with different interests and strengths.
Treat security as an enabler. Effective cybersecurity helps organisations manage risk while continuing to innovate and operate with confidence.
Keep learning and give back. Staying relevant requires ongoing development, while sharing knowledge and mentoring others can help strengthen the wider technology community.
About the UNIMY Expert Interview Series
The UNIMY Expert Interview Series brings real-world perspectives from experienced technology professionals and industry leaders to students, aspiring professionals, working adults and anyone interested in building a future in technology.
Through their career stories, industry insights and practical advice, our interviewees help readers better understand the opportunities, challenges and skills involved in working in the technology industry.
This interview is part of the UNIMY Expert Interview Series, which brings real-world perspectives from experienced technology and industry professionals to students, aspiring professionals and anyone interested in building a future in technology.